Western Australia’s multi-billion-dollar defence boom has painted a target on the state’s critical infrastructure, according to experts, leaving it directly in the crosshairs of global cyber syndicates and foreign agencies.
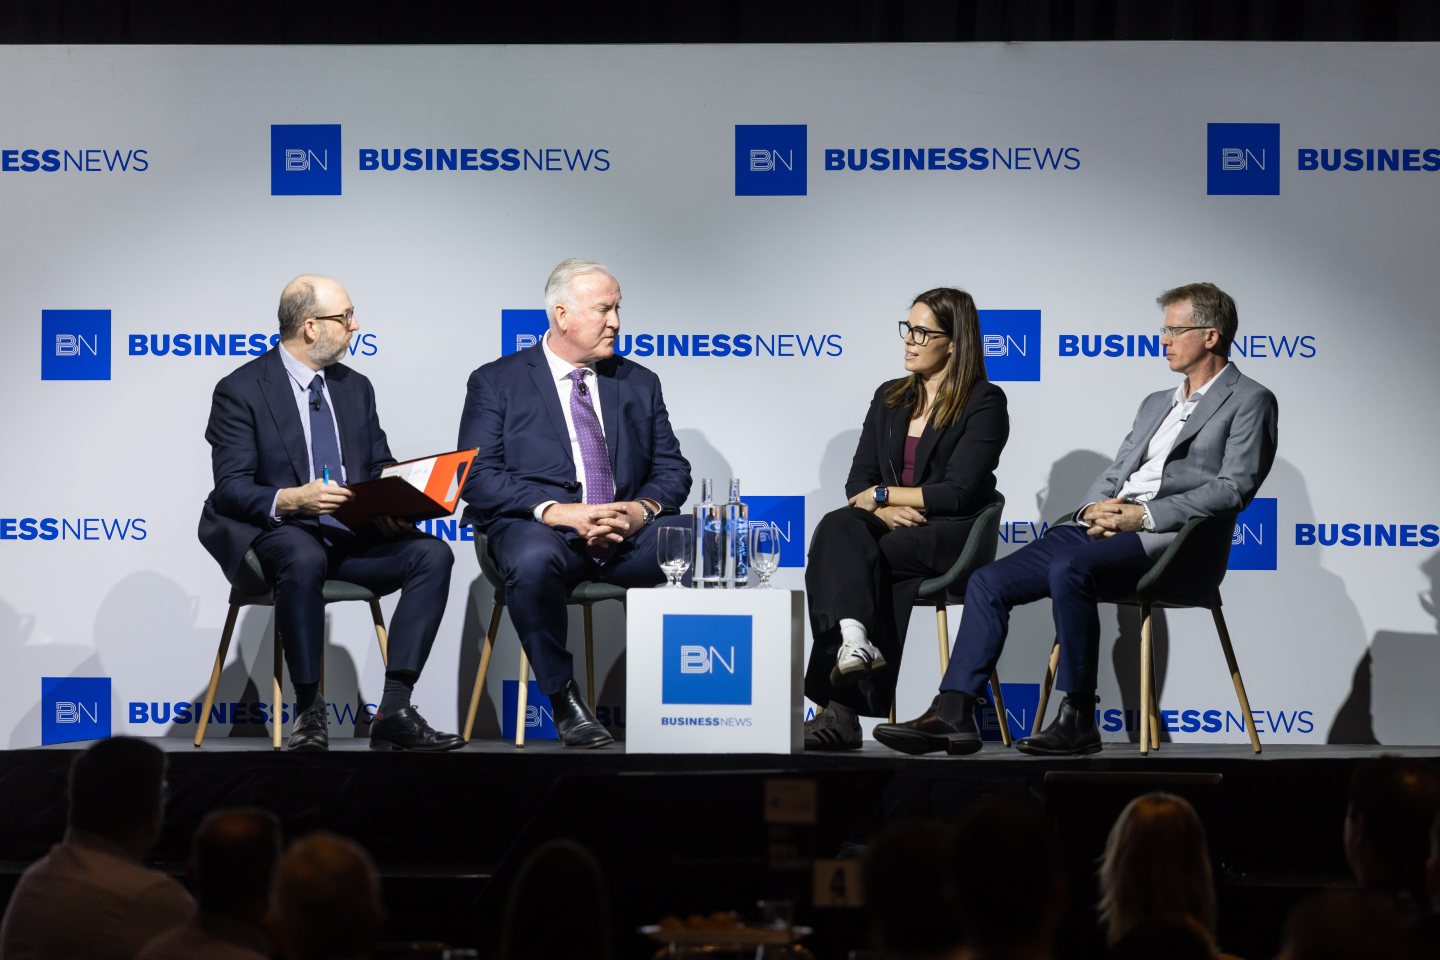
Speaking at a Business News Sector Briefing: Risk and Security on Wednesday, security leaders warned adversaries were actively monitoring WA's expansion and probing local networks for vulnerabilities.
AECOM government and defence security practice lead for Australia and New Zealand, Peter Billingham, said foreign powers were aware of the major developments unfolding across the state.
"There are quite a few nation states and smaller issue-motivated groups who have a map of Australia, and they know exactly where Perth is and what's happening, and they're actively interested in what's going on here with the defence ramp-up, for instance,” he said.
The warning coincided with revelations of a $320 million near-miss involving a local infrastructure provider.
WA Police Financial and Cyber Crime Division detective superintendent Peter Foley revealed that joint law enforcement and banking operations recently intercepted an attempted $320 million fraudulent transfer from a WA company before it could leave the country.
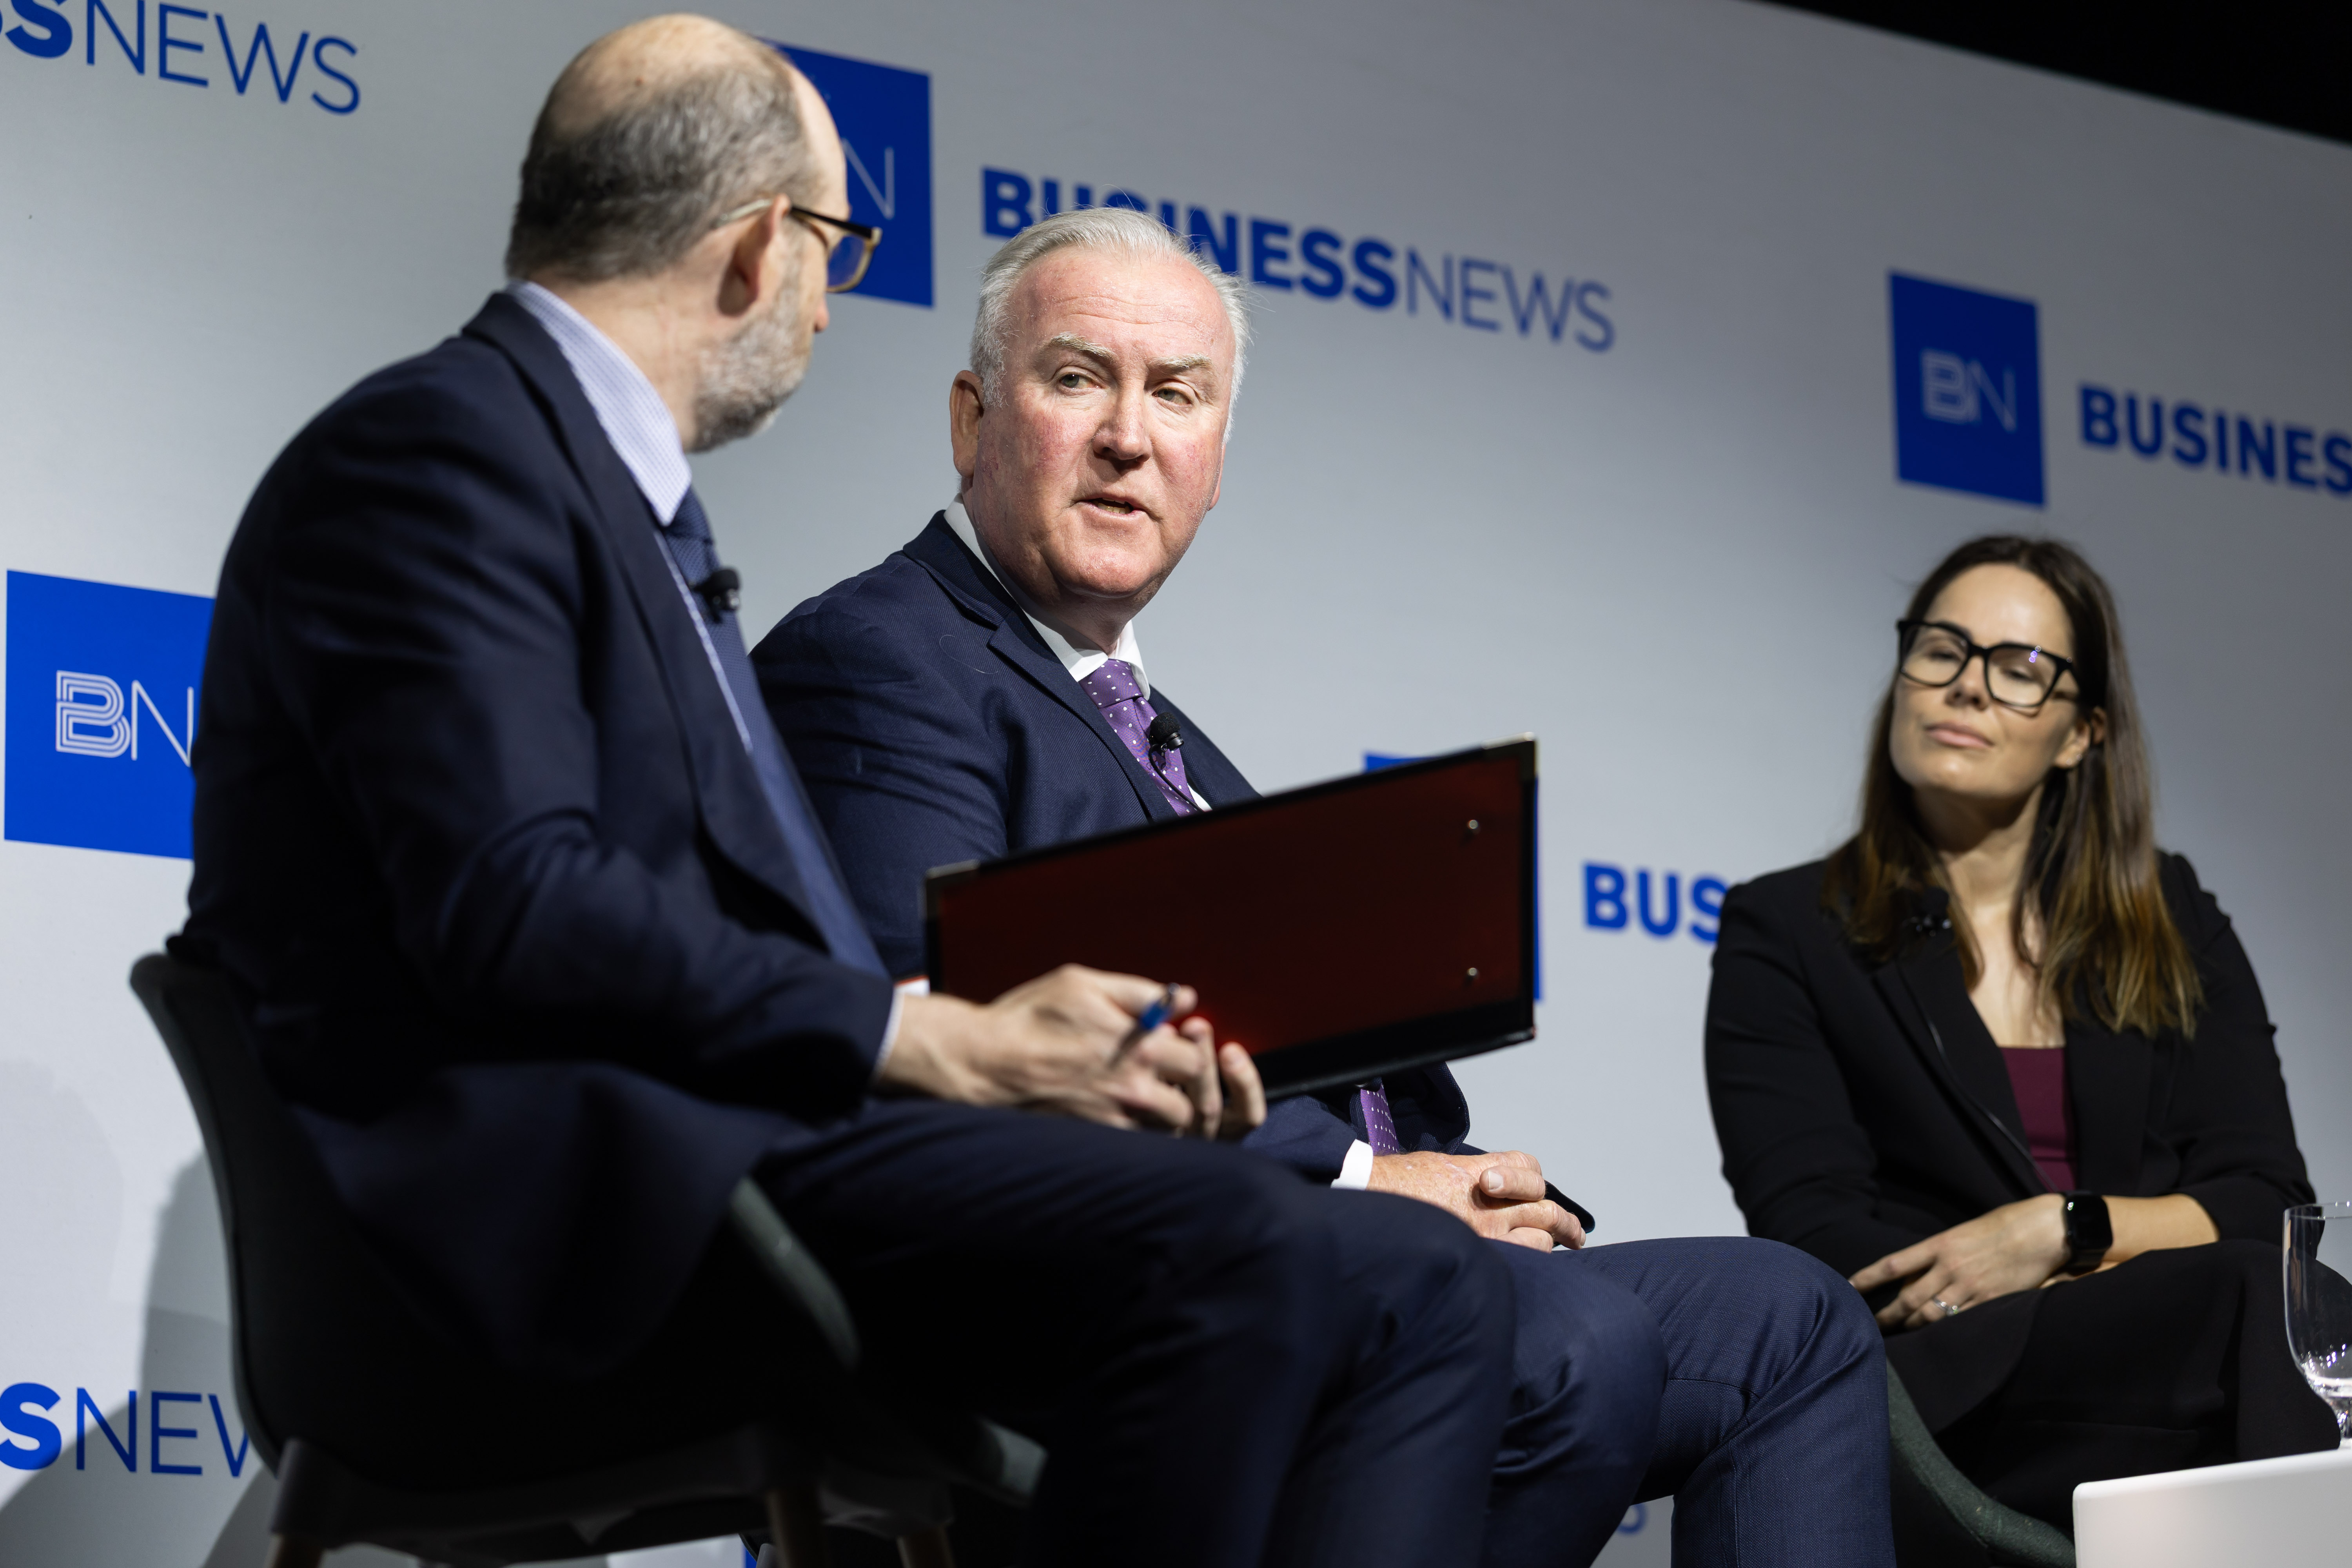
WA Police Financial and Cyber Crime Division detective superintendent Peter Foley. Photo: Matt Jelonek.
"Western Australia is loaded with very high-value transactions around business, and we have a very rich marketplace, so cyber criminals will target high cash flows," Supt Foley said.
"They like infrastructure projects; they like government funding, where invoices are received and paid."
In that case, threat actors compromised the organisation's communication flows and altered the bank account details on legitimate invoices.
The $320 million sum—split across two separate transactions—was intercepted and reversed using national kill-chain provisions coordinated through the Joint Police Cyber Coordination Centre (JPC3) just before the funds reached offshore bank accounts.
Supt Foley said cyber syndicates often succeed through simple, overlooked tactics—such as altering a single character on an invoice—to exploit fast-moving commercial approvals.
While multi-million-dollar financial fraud poses an immediate commercial hazard, panellists highlighted that the deeper danger lay in disruptions to operational technology managing ports, energy, and water supplies.
Mr Billingham cautioned that the vulnerability in critical supply chains often lay within smaller, third-party contractors rather than the primary asset owners themselves.
He pointed to the operational fallout of a back-end disruption to a major facility like the Port of Port Hedland, noting that while a large company may boast secure perimeter systems, a breach of a downstream vendor can trigger cascading shutdowns.
He added that legacy operational technology, such as programmable logic controllers running industrial sites, were never built to question commands.
"Historically, PLCs never used to ask why; they just did," Mr Billingham said.
"Because it's a lifesaver, I need to stop that conveyor straight away, not ask perhaps why this other device is asking you to do something it's never done before.
"And that's an avenue that we need to look at as well to harden our systems."
CyberCX director of cyber intelligence Leah Pinto said the convergence of geopolitical friction, third-party vendor risks, and artificial intelligence was reshaping the corporate threat profile.
Ms Pinto pointed to nation-state activity—including state-sponsored actors from countries like North Korea—actively targeting IT workers and privileged credentials on professional platforms like LinkedIn to embed themselves inside corporate networks.
“That brings in geopolitics and international conflicts, and puts a mark on your back as an organisation that manages critical infrastructure or something similar in Perth,” she said.
To illustrate how physical and non-traditional supply chains are being weaponised, Ms Pinto highlighted an unprecedented incident in France over the past few days, in which hackers sabotaged a centralised refrigeration management software across hundreds of supermarkets.
The intrusion forced commercial coolers into defrost mode, pushing temperatures to 50 degrees celsius, spoiling massive inventories of food, and halting operations across more than 300 stores.
Several fires were also caused by the incident.
“When we talk about the risk of the supply chain, we're often talking about our critical infrastructure, not something that's not traditionally critical infrastructure,” she said.
“But if we look at an attack that impacts our way of life, our economy, and stops production... We think of what are some critical services, but not about things that aren't critical services and impacts that can have."
The warnings come as research by CyberCX and Mandala projects AI-driven cyber attacks could cost Australian businesses up to $37 billion a year by 2030, with attacks set to surge ninefold as generative tools enable malicious actors to launch automated, highly tailored intrusions at scale.
Ms Pinto said Australia remained one of the top ten countries targeted by cyber extortionists worldwide, warning that executive teams must move beyond treating cyber defence merely as an IT function.